Sunil · Java / Spring Boot backend developer

Backend systems that don't fall apart under real money and real load.

Fintech and e-commerce systems built to handle concurrency, encrypted data, and failure, not just the happy path.

About
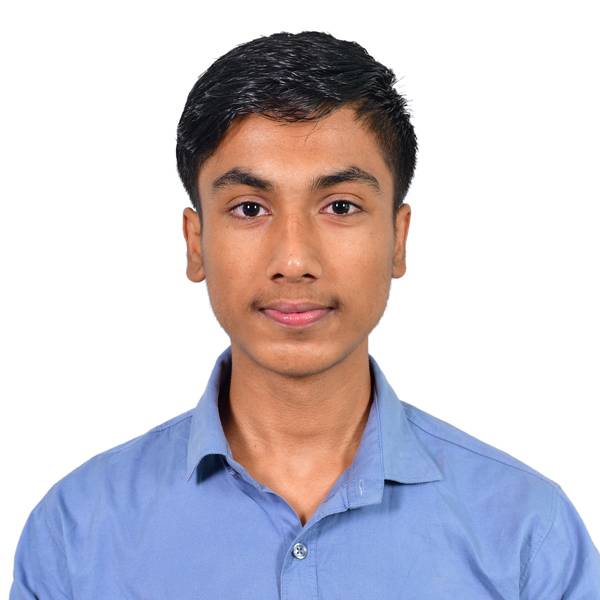
Portrait of Sunil, backend developer
Backend developer, based in Kathmandu, Nepal

I like backend work because the interesting problems aren't in the endpoint: they're in what happens when two requests hit the same row at once, when a partner's API changes underneath you, or when a queue backs up and nobody notices for an hour. That's mostly what I've spent the last couple of years on: fintech and HR systems handling real transactions and real personal data, where getting it almost right isn't good enough.

At Encrypto Tech I worked on FashionMart, a large e-commerce platform built as a team project, where I owned several modules end to end and helped shape how events and caching worked across the system.

If something here looks like the kind of problem you're dealing with, I'd like to hear about it.

Experience

Two years building production backend systems. The featured case studies below cover the work in depth.

Auth & Access ControlFintech / PaymentsEvent-Driven SystemsTesting & Reliability

Java Backend Developer

Rebooted Creation Labs, Kathmandu, Nepal

September 2024 – April 2026

  • Built eKYC with encrypted PII handling and biometric verification for a bank partner integration.
  • Designed a dynamic RBAC and commission engine used platform-wide for merchant onboarding and payouts.
  • Fixed a race condition in wallet balance updates using optimistic locking, eliminating concurrent corruption.
  • Built face-auth + QR attendance check-in/checkout and MFA-secured auth for an HR platform used company-wide.
  • Standardized error handling and wrote JUnit/Mockito coverage across success paths, edge cases, and full API-to-database flows.

Built FashionMart, an event-driven modular monolith for e-commerce, collaboratively with other backend developers. See the full case study below.

Modular MonolithEvent-Driven SystemsCaching & TracingAccess Control

Java Backend Developer

Encrypto Tech, Kathmandu, Nepal

May 2026 – September 2026

  • Owned the product, inventory, cart, support, and review modules end-to-end within a 15-module codebase, and worked jointly on the shared order module.
  • Built the outbox pattern (publisher, scheduler, event entity) for reliable Kafka delivery in the product, inventory, cart, review, and support modules.
  • Built the shared Redis/Caffeine cache adapters used for product data across the platform.
  • Added MDC-based correlation-ID tracing through the shared logging filter so requests stay traceable across modules.
  • Built the nearest-warehouse lookup that routes orders to the closest warehouse with available stock.
Selected WorkCase studies

Six projects, read as engineering problems rather than feature lists.

01

Money Transfer & Bank Partner Integration

Confidential fintech platform · Rebooted Creation Labs · Production · Team project

Problem

Domestic money transfer (DMT) requires integrating with multiple bank partners, each with their own onboarding (eKYC) and transaction APIs, while keeping customer data encrypted and processing transaction status that arrives asynchronously.

Ownership

Owned eKYC/onboarding and transaction processing for a bank partner integration, plus multi-provider sender search and commission distribution on the platform’s DMT module.

Method

Built eKYC onboarding with biometric verification and encrypted handling of customer data. Built transaction, balance, and refund endpoints with webhook-driven async status updates. Used Redis for caching and RabbitMQ for decoupled async processing.

Outcome

Shipped production KYC and transaction services for a live bank partner integration, handling real customer data and financial transactions safely.

  • Spring Boot
  • RabbitMQ
  • Redis
  • PostgreSQL
  • Webhooks
02

Merchant Admin & Access Control

Confidential fintech platform · Rebooted Creation Labs · Production · Team project

Problem

A fintech distribution platform needs a secure admin backend to onboard merchants and organizations, enforce role-based access at scale, and calculate commissions correctly.

Ownership

Primary contributor to the platform’s merchant/admin backend module.

Method

Built JWT-based auth with MFA and trusted-device management. Designed a dynamic RBAC system: roles, permissions, and menus generated per user rather than hardcoded. Built a commission engine backed by Redis-cached config and an audit trail for compliance.

Outcome

Became the team’s primary contributor to the platform’s core access-control and payout logic, now underpinning how every merchant is provisioned and paid.

  • Spring Security
  • JWT
  • MFA
  • RBAC
  • Redis
03

HR Management System

Rebooted Creation Labs · Production · Primary contributor

Problem

The company needed an internal HR platform covering secure employee auth, attendance tracking, leave/WFH management, and salary calculation, used company-wide.

Ownership

Primary contributor and owner of the auth, attendance, and role/department management modules.

Method

Built MFA-secured authentication with token rotation. Implemented face-auth and QR-based check-in/checkout with auto-checkout, plus a role/department/position hierarchy. Built leave, WFH, and salary calculation, and an employee onboarding/verification flow.

Outcome

Became the platform’s core attendance and identity system, shipped to production and used company-wide.

  • Spring Boot
  • JWT
  • MFA
  • Face-auth
  • PostgreSQL
04

FashionMart

Encrypto Tech · Modular monolith · May – September 2026

Problem

Fashion e-commerce platforms need to handle heavy read/browse traffic, spiky checkout load, and a complex multi-stage order lifecycle (returns, exchanges, trials) without different parts of the system stepping on each other’s data.

Ownership

Backend contributor on a small team, owning the product, inventory, cart, support, and review modules end-to-end within a 15-module codebase, and working jointly on the shared order module.

Method

A single Spring Boot application organized as a domain-driven modular monolith: 15 modules covering product, order, cart, inventory, payment, shipping, analytics, discount, loyalty, notification, review, support, and user, each following hexagonal architecture. Built the outbox pattern (publisher, scheduler, and event entity) end-to-end for the product, inventory, cart, review, and support modules, so Kafka events survive a crash between the database write and the publish. Built the shared Redis/Caffeine cache adapters used for product data platform-wide, and added MDC-based correlation-ID tracing through the shared logging filter so one request stays traceable as it crosses modules. JPA for writes, MyBatis for reads, GraphQL for the queries REST doesn’t fit well.

Outcome

Eliminated N+1 query patterns in product and inventory lookups by batching reads instead of querying item by item, and fixed recurring role and permission bugs across staff and warehouse access control.

  • Kafka
  • Modular Monolith
  • Hexagonal Architecture
  • JPA + MyBatis
  • GraphQL
  • Redis / Caffeine
05

CareSync

Final-Year Capstone · Solo project · Public GitHub repo

Problem

When multiple family members care for an elderly or physically unable loved one, medication coordination breaks down silently: one caregiver gives a dose, another unaware caregiver gives it again, a real overdose risk.

Ownership

Designed and built solo, full-stack, from problem definition through backend and frontend implementation.

Method

Built a shared caregiving platform where family members coordinate around one patient profile. Core mechanism: a confirmation-based logging system with real-time notifications, duplicate-dose detection, time-window validation, and a full audit trail. JWT-based auth with role-based access control. Patient-facing UI deliberately simplified for elderly users.

Outcome

A working full-stack system that turns a real, dangerous coordination gap in home caregiving into a solvable software problem.

  • React
  • Spring Boot
  • PostgreSQL
  • JWT
06

CI/CD Pipeline with Jenkins

Self-directed · Local Jenkins on Docker · Working end to end

Problem

Shipping a containerized app by hand means building the image, pushing it, SSHing somewhere, and restarting containers in the right order every single time: slow, easy to get wrong, and impossible to hand to anyone else.

Ownership

Built the entire pipeline myself against an existing open-source Django app (the app is not mine, the delivery pipeline is): Jenkinsfile, Shared Library, credentials, webhook wiring, and access control.

Method

Jenkins running as a Docker container with a persistent volume, driving a Declarative Pipeline: git clone → docker build → push to Docker Hub → multi-container deploy (app + MySQL + nginx) via Compose. Moved the Jenkinsfile into source control, wired GitHub webhooks so every push auto-triggers a build, and extracted the repeated stages into a Jenkins Shared Library living in its own repo. Credentials handled as scoped tokens rather than passwords, and access locked down with the Role-based Authorization Strategy.

Outcome

Every push to main now builds, pushes a tagged image, and redeploys with no manual step. Worked through eleven real failures on the way: missing Docker CLI inside the container, docker.sock group permissions, an outdated Buildx, credential-variable scoping inside withCredentials, and an invisible Unicode character in a filename that made a library function silently unresolvable.

  • Jenkins
  • Docker
  • Docker Compose
  • Docker Hub
  • Shared Libraries
  • Webhooks
Other ProjectsSmaller builds & experiments
  • Bank Partner Mock Server

    Spring Boot

    Simulator for a DMT partner’s API covering remitter eKYC, beneficiary management, transaction send/status, and penny-drop verification, for development and testing without a live bank partner.

  • Passkey Authentication

    Spring Boot · WebAuthn · Spring Security

    Passwordless login via WebAuthn/FIDO2 passkeys.

  • Spring Security with JWT Authentication

    Spring Boot · JWT

    Stateless auth with RBAC and secured endpoints.

  • Event-Driven Email Notifications

    Spring Boot · RabbitMQ · Thymeleaf

    Async email delivery via message queues with HTML templates.

  • AWS LocalStack Integration

    Spring Boot · Docker · LocalStack

    Local AWS simulation integrating S3 and SQS for cloud-ready development.

Skills

The stack I reach for.

Core Stack

  • Java
  • Spring Boot
  • Spring MVC
  • Spring Data JPA
  • Spring Security
  • SQL
  • PostgreSQL
  • JWT
  • REST API Design
  • Microservices
  • DDD / Hexagonal Architecture
  • Docker

Also Worked With

  • Kafka
  • RabbitMQ
  • Redis
  • MongoDB
  • MySQL
  • Hibernate
  • Keycloak (SSO/RBAC)
  • WebAuthn / Passkey
  • MFA / OTP
  • GraphQL
  • Jenkins
  • Docker Compose
  • CI/CD Pipelines
  • JUnit
  • Mockito
  • Git
  • Postman
  • Maven
  • Swagger